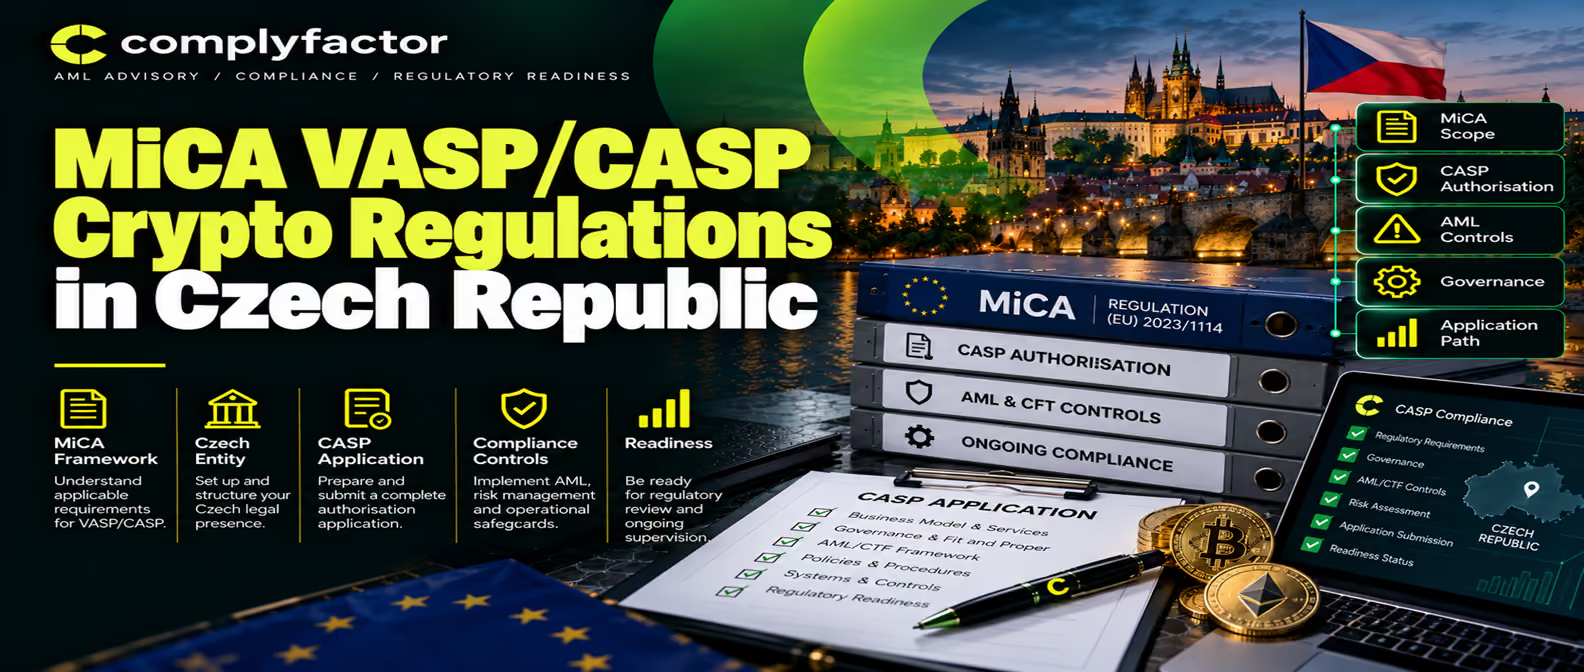
MiCA VASP/CASP Crypto Regulations in Czech Republic
A practical guide to crypto-asset service provider (CASP) authorisation in the Czech Republic: who needs it, the end of the VASP transitional period on 1 July 2026, the Czech National Bank application route, AML duties under the FAU, passporting and common mistakes.


Key takeaways
- The Czech VASP transition has ended: the transitional period for former national providers ran no later than 1 July 2026, and the CNB has ordered unauthorised providers to stop.
- The CNB is the MiCA authority: CASP applications go to the Czech National Bank, and already-regulated financial entities may notify it under Article 60.
- Substance and capital are tested: Article 59(2) requires effective management and a resident director in the Union, and Annex IV sets minimum capital of EUR 50,000, 125,000 or 150,000 by service class.
- AML runs in parallel: Czech VASPs are obliged entities under Act No. 253/2008 Coll. supervised by the FAU, with Czech-language documents and the EU travel rule.
- Passporting needs a notification: a Czech CASP informs the CNB before serving clients in other Member States under Article 65.
Short answer: crypto-asset services in the Czech Republic require MiCA authorisation from the Czech National Bank (CNB), or a prior notification by a financial entity that the CNB already supervises. The transitional period for former national providers ended on 1 July 2026. Anti-money laundering duties sit on top of authorisation and are supervised by the Financial Analytical Office (FAU). This guide explains who needs what, where the VASP-to-CASP transition stands, what a CNB application involves, and how to avoid the mistakes the CNB itself has described. Facts below are taken from the CNB, ESMA, the FAU and the text of Regulation (EU) 2023/1114, and are current as of 30 October 2026.
A crypto business in the Czech Republic that used to operate under a trade licence for virtual-asset services now faces a simple question from banks, partners and regulators: is it authorised under MiCA? Since 1 July 2026 the old national route no longer protects anyone, and the answer is either yes, with an entry in the ESMA register, or the business has to stop serving clients.
Who needs authorisation to provide crypto-asset services in the Czech Republic?
Under Article 59 of Regulation (EU) 2023/1114 (MiCA), nobody may provide crypto-asset services in the Union unless they are either a legal person or other undertaking authorised as a crypto-asset service provider (CASP) under Article 63, or a credit institution, central securities depository, investment firm, market operator, electronic money institution, UCITS management company or alternative investment fund manager that may provide those services through the Article 60 notification.
The CNB describes its role as the Czech competent authority for MiCA. It receives CASP applications, and it receives notifications from entities it already authorises: credit institutions, central securities depositories, investment firms, electronic money institutions, management companies and regulated market operators.
In practice a Czech business falls into one of three groups:
- Crypto-native firm without another licence. It needs CASP authorisation from the CNB before providing custody, exchange, trading platform operation, transfer, advice, portfolio management or any other MiCA service.
- Already authorised financial entity. A bank, investment firm, electronic money institution or similar entity may add crypto-asset services by notifying the CNB under Article 60 before it starts. For credit institutions and central securities depositories the notification must be made at least 40 working days before the first service.
- Firm based outside the EU. It cannot serve Czech or other EU clients without authorisation, apart from the narrow reverse solicitation exception covered below.
Article 59(2) sets further requirements for Czech applicants. A CASP authorised under Article 63 must have its registered office in a Member State where it carries out at least part of its services, its place of effective management in the Union, and at least one director resident in the Union. A Czech registered office on paper does not meet that standard on its own.
VASP to CASP: where the Czech transition stands
Before MiCA, Czech virtual-asset businesses worked under a trade licence. The FAU describes this as a notifiable unqualified trade, field no. 81, provision of services related to virtual assets, under the Trade Licensing Act. MiCA let Member States run a grandfathering period of up to 18 months. ESMA's list of grandfathering periods shows 18 months for the Czech Republic and notes that applicants had to apply before 31 July 2025 to benefit.
The key dates, as published by the CNB, ESMA and the Regulation:
- 30 December 2024. MiCA applied in full. Providers that had operated lawfully before this date could use the transitional regime under Article 143(3).
- 15 February 2025. The CNB became the competent authority and the previous national regime ended that day, according to the CNB press release of 11 February 2026.
- 31 July 2025. Last day to file a CASP application to continue under the transitional regime. From August 2025 only legal entities could continue, not natural persons.
- 11 February 2026. The CNB issued its first six MiCA authorisations and reported 248 applications, most of them filed at the end of July 2025.
- 1 July 2026. The transitional period ended. Applicants who had filed on time could operate until the CNB decided, but no later than this date.
- 19 October 2026. The CNB reported 11 authorised domestic CASPs and five new applications since 1 July 2026, two of them repeat applications. Proceedings are ongoing.
What this means today: a former trade-licence holder that has no CNB authorisation and no pending decision is no longer covered. The CNB press release of 19 October 2026 states that firms which kept providing services without authorisation were ordered to stop. The CNB lists fines, suspension or prohibition of services and marketing, and orders to cease activity among its tools. Suspected fraud or money laundering is referred to the Police of the Czech Republic and the FAU.
ESMA took the same line at EU level. Its public statement of 23 June 2026 says unauthorised providers should stop onboarding new clients, limit activity to what an orderly exit needs, tell clients clearly about wind-down plans, and keep AML/CFT controls running throughout. A new application today is a fresh authorisation procedure with no grandfathering cover during the review.
The CNB authorisation route under Articles 62 and 63
A legal person that intends to provide crypto-asset services applies to the competent authority of its home Member State. For a Czech applicant that is the CNB. Article 62(2) sets the minimum content of the application. It includes:
- the applicant's name, legal entity identifier, website and contact details, plus its legal form and articles of association;
- a programme of operations that sets out the services it intends to provide and where and how it will market them;
- proof that it meets the prudential safeguards required by Article 67;
- a description of governance arrangements and proof that members of the management body are of sufficiently good repute and have the knowledge, skills and experience to manage the provider;
- the identity of shareholders and members with qualifying holdings;
- a description of internal control mechanisms, policies and procedures to identify, assess and manage risks;
- technical documentation of ICT systems and security arrangements, with a non-technical description;
- the procedure for segregating clients' crypto-assets and funds, and the complaints-handling procedure;
- service-specific information, for example custody policy, trading platform operating rules, exchange policy or order execution policy, depending on the services planned.
The Commission has set out the detailed content and forms in Delegated Regulation (EU) 2025/305 and Implementing Regulation (EU) 2025/306, both listed on the CNB's crypto-asset legislation page. Use those templates as the structure for the file.
Statutory timing
Under Article 63 the CNB must acknowledge receipt within five working days and, within 25 working days, assess whether the application is complete. If it is not, the CNB sets a deadline for the missing information and may refuse to review an application that is still incomplete when the deadline passes. Once the application is complete, the CNB has 40 working days to assess compliance and adopt a fully reasoned decision granting or refusing authorisation, and it must notify the applicant within five working days of that decision. The clock starts with a complete application, so the time an applicant needs to prepare a credible file and to answer questions comes on top of these periods.
Minimum capital and prudential safeguards
Article 67 requires prudential safeguards equal to the higher of the permanent minimum capital in Annex IV and one quarter of the fixed overheads of the preceding year. Annex IV sets three classes:
- Class 1, EUR 50,000: execution of orders, placing, transfer services, reception and transmission of orders, advice and portfolio management.
- Class 2, EUR 125,000: everything in class 1 plus custody and administration, and exchange of crypto-assets for funds or for other crypto-assets.
- Class 3, EUR 150,000: everything in class 2 plus operation of a trading platform.
A provider that has not yet been in business for a year uses the projected fixed overheads for its first 12 months, as submitted with the application.
What the CNB says it looks for
In its release on its first 11 authorisations the CNB said it assesses the provider itself, including risk management, internal controls, organisational arrangements and capital. It also reported that a significant share of applications were wholly insufficient and lacked essential information and documents, and that many came from entities with no verifiable track record, virtual registered offices or plans to operate abroad. Only a very small share showed a realistic and transparent business model, ownership structure and financing method. The CNB also stated that authorisation is not an endorsement of any crypto-asset investment.
One further point from Article 63: before it decides, the CNB may consult AML authorities and financial intelligence units to check whether the applicant has been the subject of an investigation into money laundering or terrorist financing. Past conduct of the applicant and of its owners therefore matters to the file.
Anti-money laundering obligations in the Czech Republic
Authorisation under MiCA and AML supervision are separate regimes. The FAU states that virtual asset service providers are obliged entities under the Czech AML Act, Act No. 253/2008 Coll., classified as financial institutions. The FAU is the AML/CFT supervisor and receives suspicious transaction reports. The FAU does not keep a register of VASPs and the authorisation itself comes from the CNB.
The FAU's guidance for VASPs lists these duties:
- appoint a contact person under section 22 of the AML Act and notify the FAU, within 30 days of becoming an obliged entity and within 15 days of a change, through the data box using the FAU form;
- prepare a written risk assessment within 60 days of becoming an obliged entity and keep it updated;
- prepare a written system of internal rules, policies and controls within 60 days, based on the risk assessment;
- identify and carry out due diligence on customers, keep records and train employees;
- report suspicious transactions to the FAU without undue delay, with strict confidentiality about the report.
The FAU also states that submissions to it must be in Czech or Slovak, that the risk assessment and internal rules must be in Czech, and that the contact person must be able to communicate with the FAU in Czech or Slovak. That affects who a foreign-owned CASP can appoint locally.
The EU travel rule applies as well. According to the FAU, from 30 December 2024 VASPs in the Czech Republic are bound by Regulation (EU) 2023/1113 on information accompanying transfers of funds and certain crypto-assets. The CNB and ESMA both stress that AML/CFT checks continue during any wind-down or client migration, and a CASP that receives clients from a provider that is closing must complete its own onboarding checks.
Passporting a Czech CASP authorisation into other EU states
A CASP authorised in the Czech Republic may serve clients in other Member States under Article 65. It sends the CNB a list of the Member States, the services it will provide there, the planned start date and a list of its other activities not covered by MiCA. The CNB passes the information to the host Member States, ESMA and EBA within 10 working days. The provider may begin from the date it receives the CNB's communication, or at the latest from the 15th calendar day after it submitted the information.
The same single market works in the other direction. The CNB confirmed that providers authorised in another Member State may serve Czech clients, and that authorised entities can offer services across the EU after notifying their intention. Anyone checking a counterparty should search the ESMA interim MiCA register for the entity name, its home authority and the services it is authorised to provide.
Reverse solicitation: a narrow exception
Article 61 says the authorisation requirement does not apply where a client in the Union initiates a service at its own exclusive initiative with a third-country firm. If the firm, or anyone acting for it, solicits clients or prospective clients in the Union by any means, the service is not treated as client-initiated, whatever a contract or disclaimer says. Client initiative also does not allow the firm to market new types of crypto-assets or services to that client.
ESMA's guidelines on reverse solicitation of 26 February 2025 read solicitation broadly and technology-neutrally and read the exclusive-initiative exception narrowly. They treat a website in an EU official language, geo-targeted advertising, sponsorship of national events, and paid influencers as indicators of solicitation. Firms should record who initiated each service. A non-EU platform that wants Czech clients should plan for authorisation instead of relying on this exception.
Practical checklist for a Czech CASP application
- Confirm which services you provide and which Annex IV class applies. Map each service to a MiCA service definition before drafting anything.
- Decide the route: CASP authorisation under Article 63, or Article 60 notification if you already hold a licence the CNB supervises.
- Set up the entity: legal person, real registered office in a Member State where you provide services, place of effective management in the Union, and at least one director resident in the Union.
- Document the business model in a programme of operations: services, target markets, how and where you will market, revenue sources and a financial forecast that supports the prudential calculation.
- Prepare the ownership and control file: all qualifying holders, ultimate beneficial owners, source of funds and group structure.
- Evidence management body suitability: CVs, references, track record and time commitment of each director.
- Write the policies the application calls for: internal control framework, segregation of client assets, complaints, conflicts, custody or execution policies as relevant.
- Assemble ICT documentation and a plain-language summary of security arrangements.
- Build the AML framework in Czech: risk assessment, internal rules, contact person, suspicious transaction procedure, travel rule workflow.
- Check the file against Delegated Regulation (EU) 2025/305 and the forms in Implementing Regulation (EU) 2025/306 before submission.
- Plan for questions from the CNB and allocate people who can answer them within the deadline it sets.
- After authorisation, confirm your entry in the ESMA register and file any Article 65 notification before you serve clients in other Member States.
Common mistakes
- Treating a trade licence as authorisation. Transitional cover ended on 1 July 2026, and a filing made earlier gives no protection once the CNB has decided or that date has passed.
- Filing before the file is ready. The CNB has said many applications lacked essential information and documents. An incomplete application can be refused review once the deadline for missing information passes.
- A virtual office and a nominee board. Article 59(2) requires a real registered office, effective management and a resident director in the Union. The CNB has pointed to virtual registered offices as a weakness.
- An unclear business model. The CNB wants a transparent ownership structure and a realistic financing method, and a forecast that supports the own-funds calculation.
- Leaving AML until after approval. The FAU timelines run from the date you become an obliged entity, and the CNB can ask AML authorities about the applicant.
- Marketing into the EU from outside it. Geo-targeted ads and EU-language sites can defeat a reverse solicitation argument.
- Assuming passporting is automatic. The Article 65 notification must be made before you start in another Member State.
- Repeat applications without fixing the cause. The CNB noted that some entities applied several times. Address the deficiencies behind a refusal or an incomplete file before filing again.
Where ComplyFactor can help
ComplyFactor is a Canadian AML compliance advisory firm, and its team can support businesses with AML program design and independent review work. For related EU reading see our guides on CASP authorisation in Lithuania and the EU MiCA framework. Questions on the licensing decision itself should go to the CNB or to Czech-qualified counsel.
Official sources used
- Regulation (EU) 2023/1114 (MiCA), Articles 59 to 65, 67 and 143, Annex IV, Official Journal L 150, 9 June 2023.
- CNB press release, first six MiCA authorisations, 11 February 2026.
- CNB press release, 11 crypto licences, published after the 1 July 2026 end of the transitional period.
- CNB press release, three months after the transitional period, 19 October 2026.
- ESMA public statement on the end of the transitional period, 23 June 2026.
- FAU information for VASPs as obliged entities, checked 30 October 2026.
ComplyFactor specializes in FINTRAC MSB and PSP registration, independent AML effectiveness reviews, and compliance program design for Canadian and foreign money services businesses, payment service providers, fintechs, and virtual asset service providers.


Related insights
Book a free Canada AML consultation
Tell us about your business and we'll confirm which services you need — free, no obligation, 30 minutes.